Keep control of your applications and data.
A business application should reflect your responsibilities and constraints. With UERP.AI, access, data, hosting and connections are considered from the start of each project.
Early access on request · Technical arrangements are defined for each project.
A clear foundation to move forward with confidence.
Security starts with choices suited to the people, information and tools involved.
Data location
Hosting in France or elsewhere in Europe can be considered according to your needs and the chosen architecture.
Roles and access
Define the profiles and permissions people need to work with information relevant to their role.
Managed connections
Scope exchanges with existing tools, the data involved and the permissions for each integration.
The right information for the right person.
An application can bring teams together without giving everyone the same rights. Roles, views and approval steps are configured around your organization and processes.
- Identify users and responsibilities
- Define access to screens and data
- Specify who may edit or approve each step
Exact permissions are defined and tested for each application.
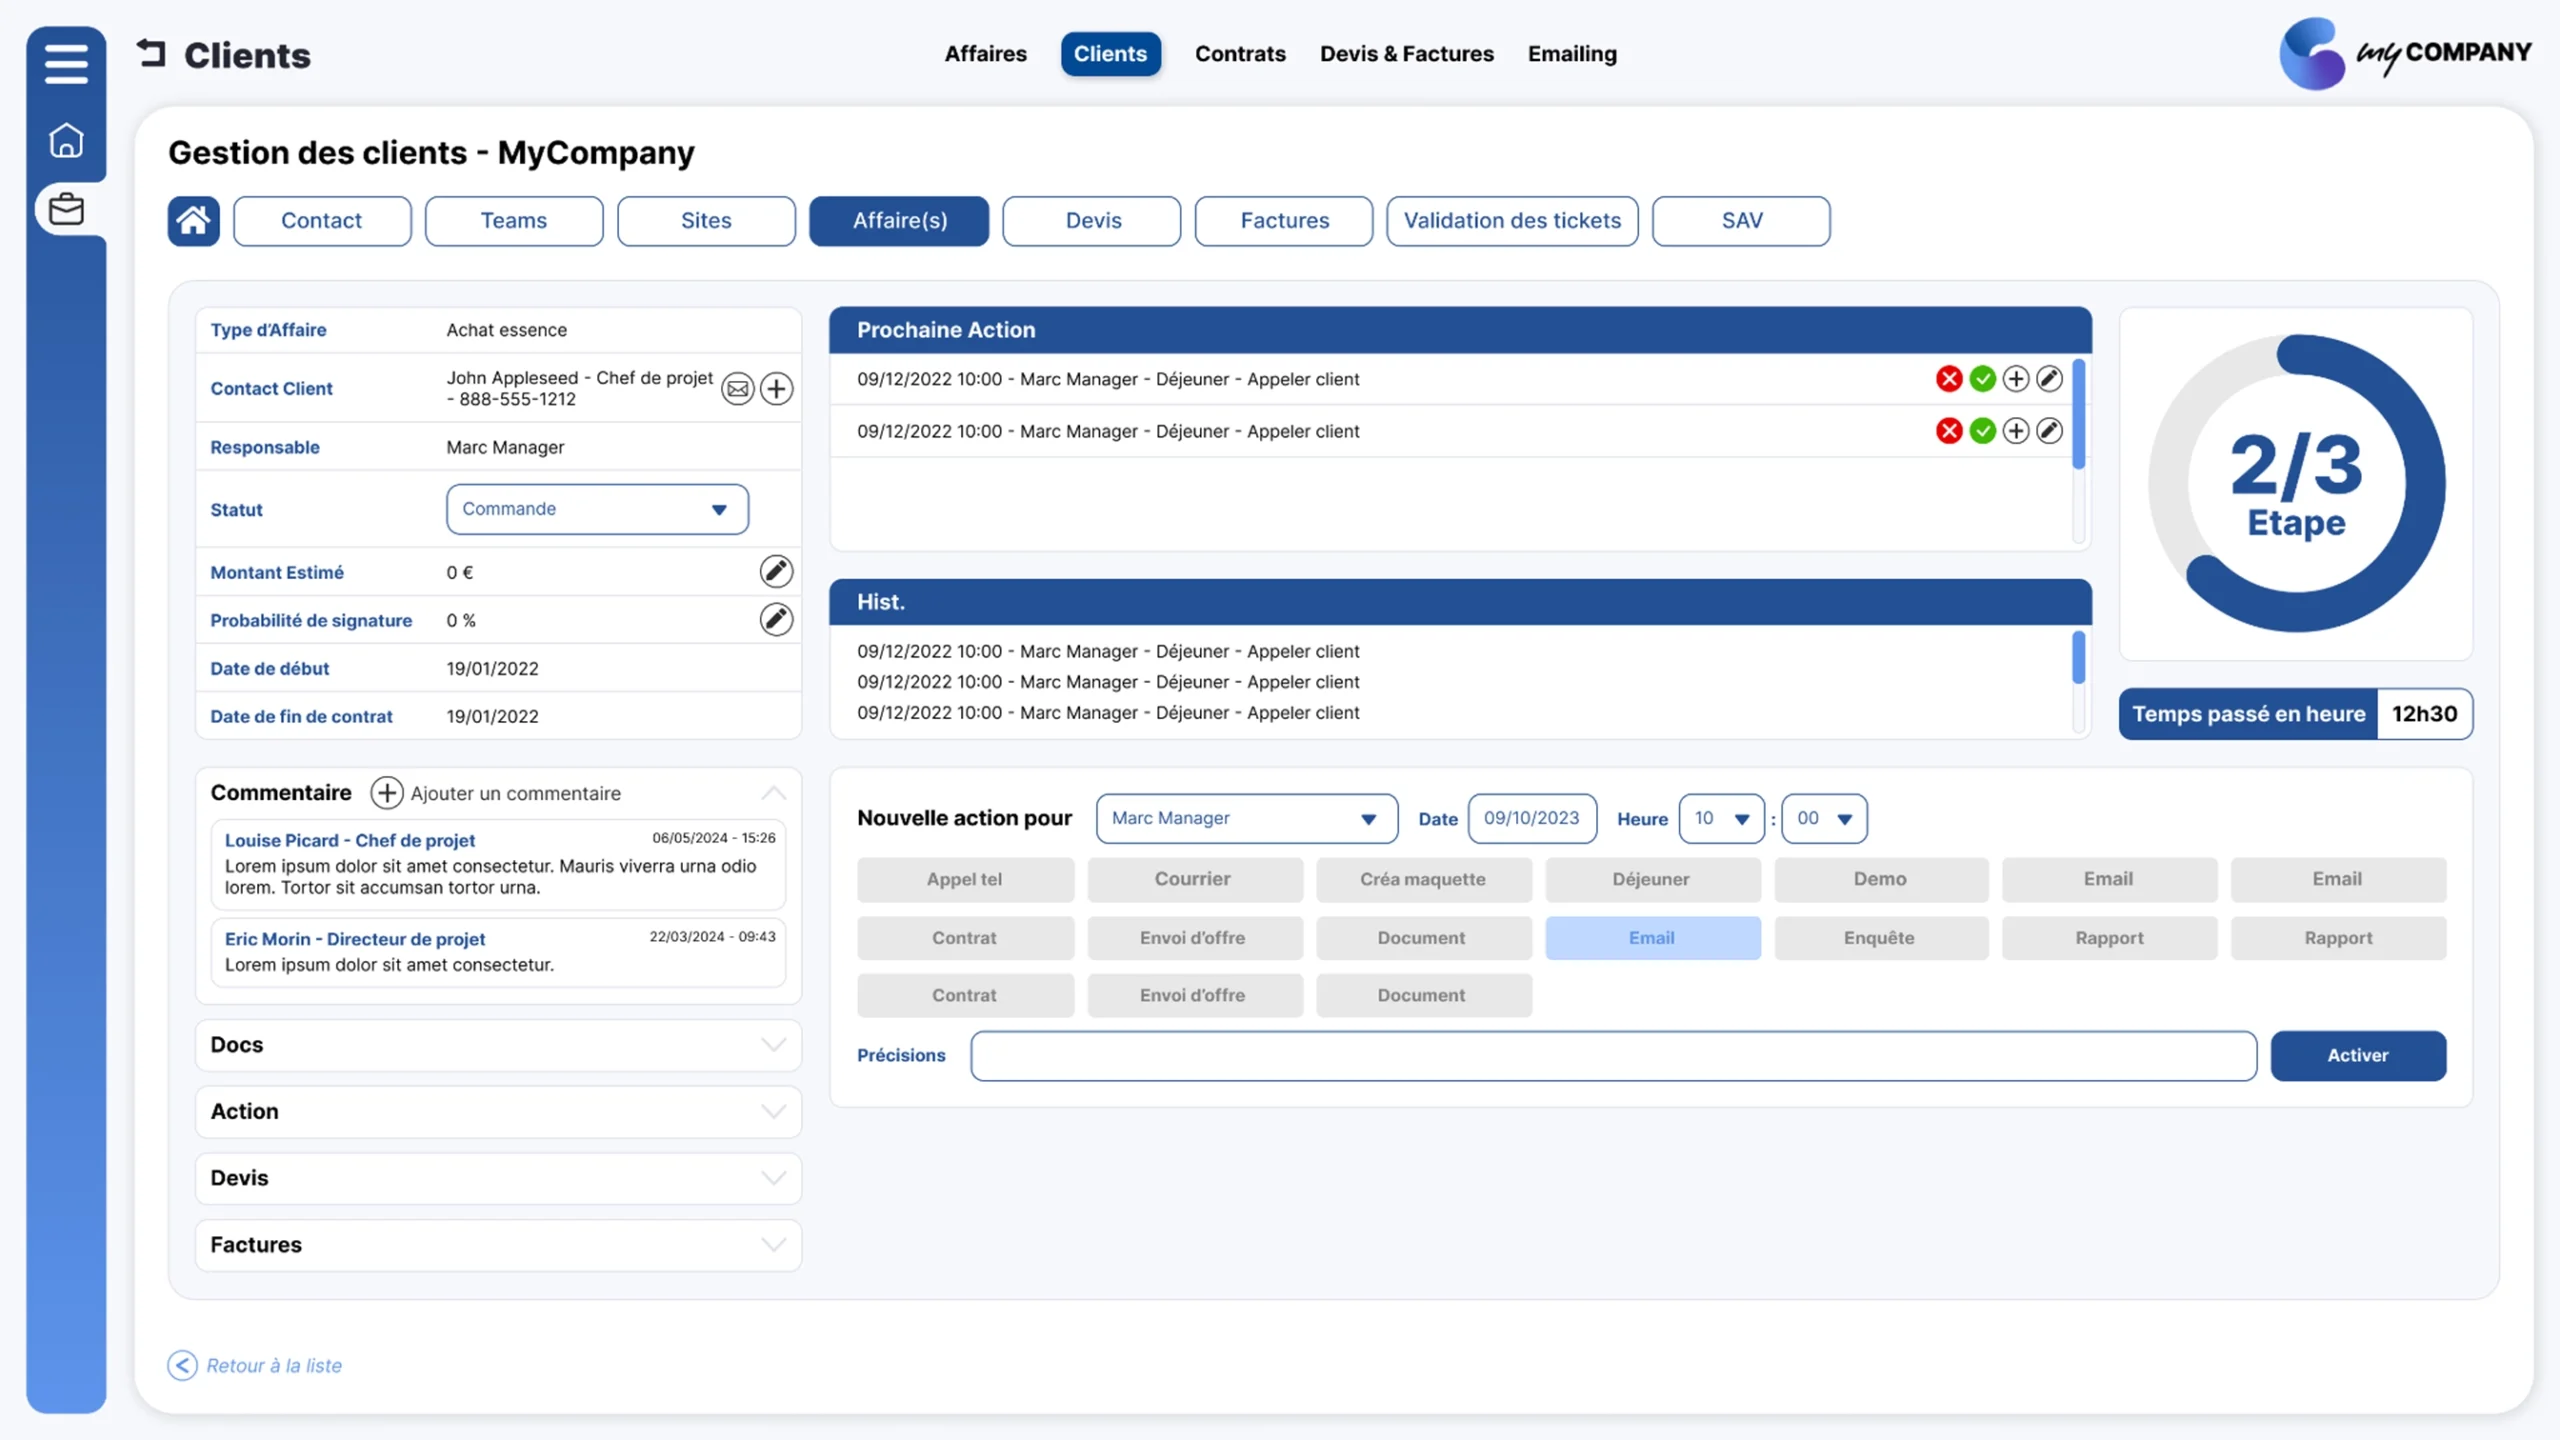
Explanatory diagram, not a standard product permissions matrix.
Consider GDPR requirements when scoping the project.
The data needed, its use, authorized users and retention periods should be reviewed for each application. Processing arrangements and the responsibilities of your organization, UERP.AI and any providers must be clarified for the chosen setup.
Hosting data in France or Europe does not, by itself, establish compliance. Data flows, providers and appropriate measures also need to be assessed.
The scope and applicable commitments are set out in project documentation.
Technical choices shaped by your context.
Hosting, deployment and API exchanges are reviewed alongside the tools to connect and your organization’s requirements. Details are confirmed during project scoping.
Choose hosting
Specify the hosting location and services needed for the project.
Define data flows
Identify exchanged data, connected systems and the required permissions.
Test before rollout
Review user journeys, roles and connections before expanding use.
Answers to define for your project.
Can my data be hosted in France or Europe?
This can be considered depending on the architecture and services selected. The hosting location and providers need to be confirmed for your application.
How do I manage team access?
Roles, permissions and approval steps are defined around your users and their responsibilities.
Does UERP.AI alone ensure GDPR compliance?
No. Compliance depends on the processing activities, data and responsibilities of each party. These points need to be reviewed for the project.
What security certifications does UERP.AI hold?
The UERP.AI team can clarify the evidence and commitments applicable to the proposed architecture.
Let’s discuss your requirements from the start.
Tell us about the data, users and tools involved. The UERP.AI team can work through hosting options, access and integrations with you.